What happened at ONECARD and 1PAY?
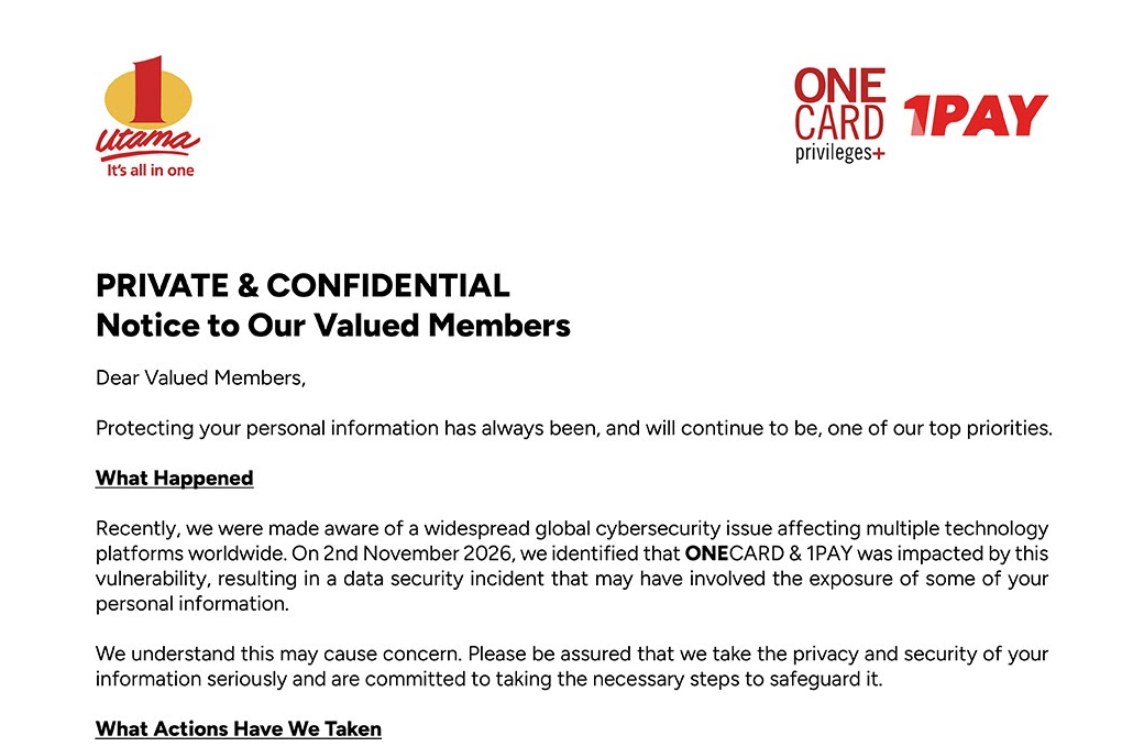
In a notice to members, the management of Bandar Utama City Centre Sdn Bhd, which runs 1 Utama’s ONECARD Privileges+ loyalty card and the 1PAY e-wallet, said it was made aware of a widespread global cybersecurity issue affecting multiple technology platforms. On 2 November 2026 it identified that ONECARD and 1PAY were impacted by this vulnerability, resulting in a data security incident that may have exposed some members’ personal information.
What personal information may have been exposed?
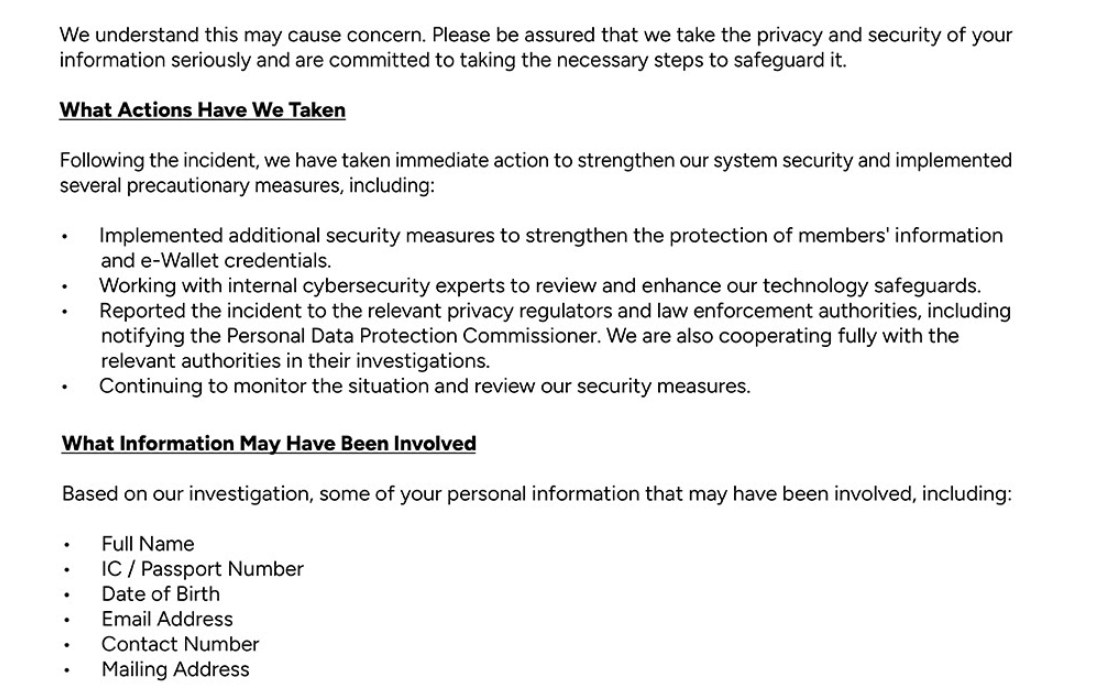
According to the notice, the information that may have been involved includes:
- Full name
- IC or passport number
- Date of birth
- Email address
- Contact number
- Mailing address
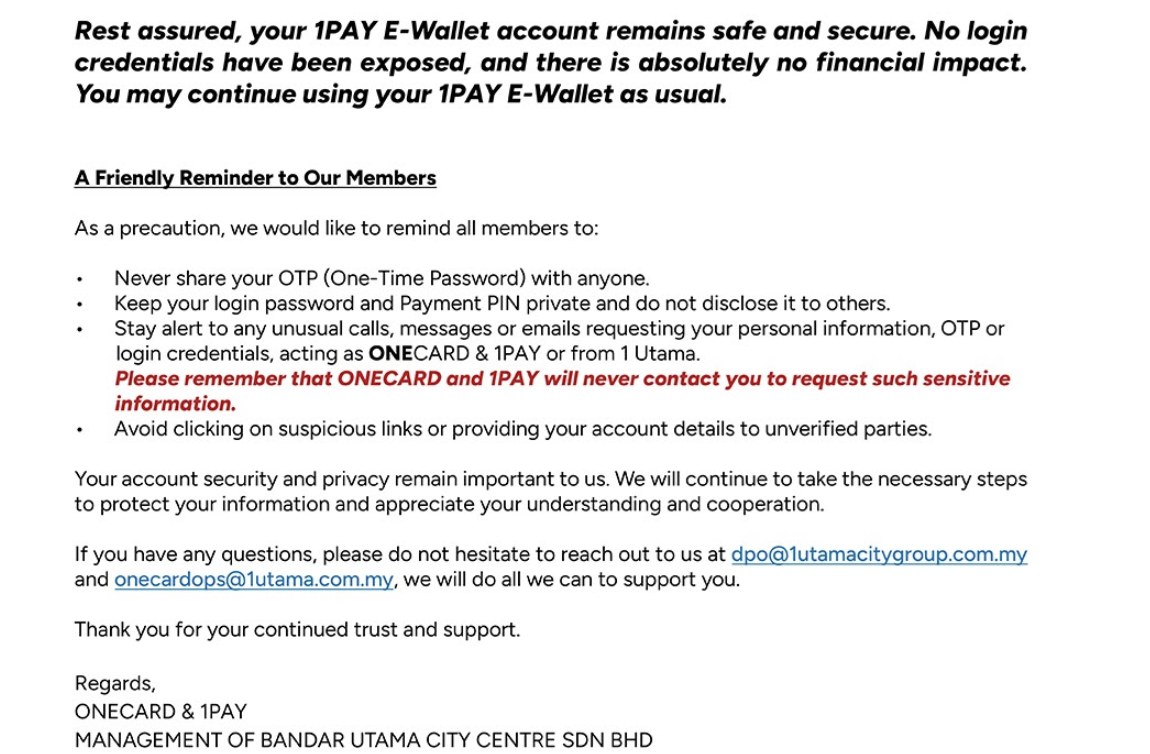
The notice states: “Rest assured, your 1PAY E-Wallet account remains safe and secure. No login credentials have been exposed, and there is absolutely no financial impact.”
What has 1 Utama done about it?
- Added security measures to protect members’ information and e-wallet credentials.
- Brought in cybersecurity experts to review its technology safeguards.
- Reported the incident to the relevant privacy regulators and law enforcement, including the Personal Data Protection Commissioner, and is cooperating with their investigations.
- Continues to monitor the situation.
Why does this matter if no money was taken?
Your name, IC number, birthday, phone number and address together are exactly what scammers need to sound convincing. A caller who already knows your IC number and address can pretend to be a bank, the police, LHDN, a courier or 1 Utama itself. These details can also be misused to try to open accounts or take loans in your name. The danger is not this week only: leaked data can be used for months.
What should ONECARD and 1PAY members do now?
- Never share an OTP, TAC or PIN with anyone, whatever they say. ONECARD and 1PAY say they will never contact you to ask for such information, and neither will your bank, broker or the police.
- Treat calls and messages that quote your details with suspicion. Knowing your IC number does not make a caller genuine. Hang up and call the company on its official number.
- Do not click links in SMS, WhatsApp or email messages about ONECARD, 1PAY, parcels, refunds or rewards.
- Check your credit report for loans or credit cards you did not apply for: Bank Negara’s free eCCRIS report, or CTOS.
- Turn on transaction alerts for your bank accounts, cards and e-wallets, and check them regularly.
- Change passwords you reused. The notice says no login credentials were exposed, but if your ONECARD or 1PAY password is the same as elsewhere, change it anyway.
- If you are scammed, act fast: call the National Scam Response Centre at 997 and your bank immediately.
Investors: protect your trading and CDS accounts too
Scammers often pose as remisiers, “investment advisers” or Bursa staff. With your IC number they may try to get you to log in to a fake trading site or give them an OTP.
- Log in to your trading app only from the official app or website, never from a link. See our M+ Global login guide.
- Check what is in your CDS account yourself with the Bursa Anywhere app, so no one can tell you your shares are “frozen” or need a fee to release.
- Check that anyone offering investment services is licensed: how to check if your remisier is licensed.
- M+ Global clients who get a suspicious call about their account can WhatsApp Dexter to check before doing anything.
Who can members contact?
The notice lists two email addresses for questions: dpo@1utamacitygroup.com.my (the data protection officer) and onecardops@1utama.com.my.
Frequently Asked Questions
Was my 1PAY money stolen?
The notice says 1PAY e-wallet accounts remain safe, no login credentials were exposed and there is no financial impact. Keep checking your transactions anyway.
What information was leaked in the ONECARD breach?
Possibly full name, IC or passport number, date of birth, email address, contact number and mailing address, according to the notice.
Do I need to cancel my ONECARD?
The notice does not ask members to cancel or change anything. The main thing is to watch out for scams that use your personal details.
What do I do if a scammer calls me using my details?
Hang up, do not share any OTP or PIN, and report it. If you have lost money, call the National Scam Response Centre at 997 and your bank straight away.
Source: ONECARD & 1PAY notice to members from the Management of Bandar Utama City Centre Sdn Bhd, November 2026 (images above). This article is based only on that notice; details may change as the investigation continues.
Disclaimer: This article is for information only. Dexter Chia is a licensed dealer’s representative (R336) at Malacca Securities (M+ Global) and is not connected to 1 Utama, ONECARD or 1PAY.